Azure Active Directory
-
Incident Response Foundations – Identity
In today’s post I talk about responding to a compromised identity in Microsoft Entra ID. There is a lot of advice floating around on what to do and how to respond; I’m bringing experiences and existing guidelines together to provide a solid foundational starting point for identity based incident response in this post.
-
Strengthening Cybersecurity: Protecting Against 99% of Attacks
In the ever-evolving landscape of cybersecurity, one undeniable truth stands out—implementing fundamental security hygiene practices can thwart the vast majority of cyberattacks. By adhering to these minimum-security standards, it is possible to protect against over 99 percent of attacks. In this article, we’ll delve into these essential practices and explore how they can fortify your…
-
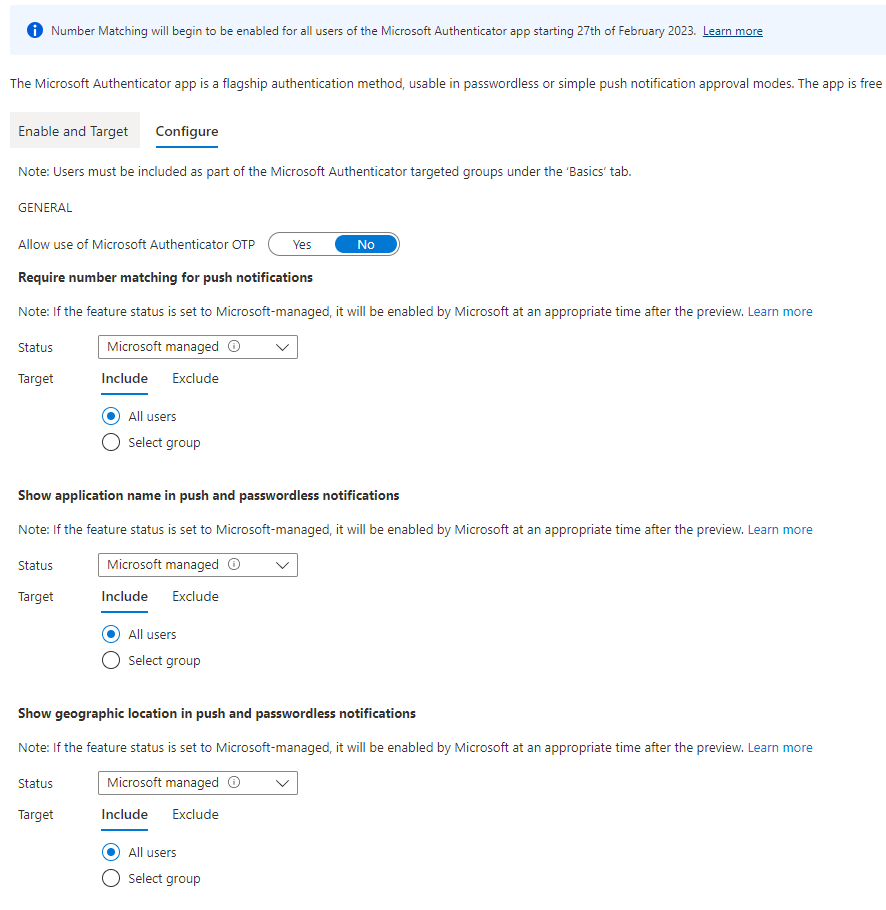
Modernize your Microsoft Authenticator Policies
Getting ready to move into Azure Active Directory or make changes to your Microsoft Entra configurations? The last few weeks I’ve talked about MFA and conditional access rules; so this week we will look at the preview for Microsoft Authenticator Policies, then change gears and talk about how to get our users excited about these…
-
Migrate Azure Multi-Factor Authentication Server to cloud-based Azure MFA
With the end of support for Azure MFA server on-premises coming soon, it’s time to start planning the move to Azure cloud-based MFA. Let’s look at the steps to starting our migration to Azure AD MFA.
-
Ready to modernize your MFA?
Just using MFA in it’s basic form is not enough. Today, we take a trip through modern authentication methods, modernizing, and becoming more phish-resistant. I talk top 3 challenges and how to tackle them together!
-
Where to find Incident Investigation Artifacts in M365 – Part 2 – The Portals
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Let’s explore the different portals where we can quickly explore our data and perform investigations…
-
Where to find Incident Investigation Artifacts in M365
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Microsoft Defender tools are capable of collecting a lot of data, and that can create questions during investigations of where is all this data and how do I find it quickly? Join me for…
-
Deploy a Log Analytics Workspace
A log analytics workspace is an environment that is made especially for storing log data. This can be Azure Monitor, or other diagnostic log data. We’ll cover a few different uses for log analytics data in this article and how to get data into your workspace. Know that each workspace has it’s own data repository,…
-
Azure Updates – Number 29 – January 29, 2022
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes. Released January 29, 2022.
-
Evaluate Microsoft Defender for Endpoint – Part 3
n this third article in our mini-series on setting up a Microsoft Defender for Endpoint labs environment we will be getting things running this week by adding devices and deploying simulations into the labs environment. This will effectively be like sending viruses out to our devices inside the labs simulator! Let’s do what we always…