retention
-
Building a Microsoft Sentinel Data Use Case
Join me this week to gain an in-depth understanding on how to clearly define what data to retain. Data retention is not just a regulatory box to tick; it’s the backbone of a robust security posture. In the realm of Microsoft Sentinel, understanding how to manage your data retention is key to leveraging the full…
-
Data Retention in Sentinel – Where to Start
Join me for as we explore one of the critical aspects of using Microsoft Sentinel — understanding data retention and how to get started. Data retention in Microsoft Sentinel involves managing how long data is kept within your Log Analytics workspace. This is crucial for compliance, incident response, log searchability, and cost management.
-
Azure Updates – Number 91 – June 1, 2024
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Enhancing Microsoft Sentinel: Part 3 – Ongoing Optimization and Staying Ahead of Threats
Join me for the final article in the min-series on Enhancing Microsoft Sentinel. Today, we review ongoing optimizations and how to stay ahead of emerging threats.
-
Enhancing Microsoft Sentinel: Part 2 – Advanced Customization and Threat Hunting
Join me for Part 2 of 3 where we review advanced customizations in Microsoft Sentinel. We review some of the steps to advance your threat hunting and better protect your environment.
-
Enhancing Microsoft Sentinel: Part 1 – Building a Stronger Foundation
Join me for Part 1 of 3 where we review Building a Stronger Foundation in Microsoft Sentinel. We review the steps to help review and build a stronger SIEM solution together.
-
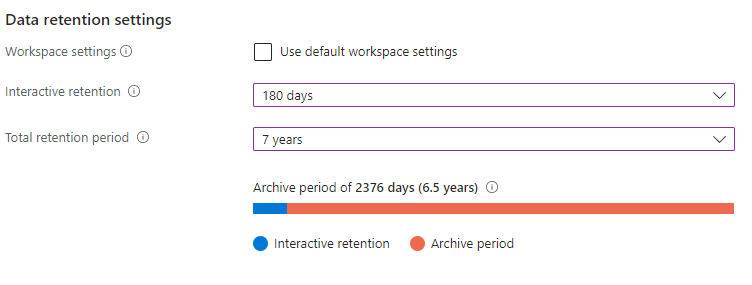
Cost Management & Microsoft Sentinel Part 2
Today we explore additional cost management options to use as part of your ongoing governance in Microsoft Sentinel. Let’s dive into the world of Log Analytics Workspace configurations together!
-
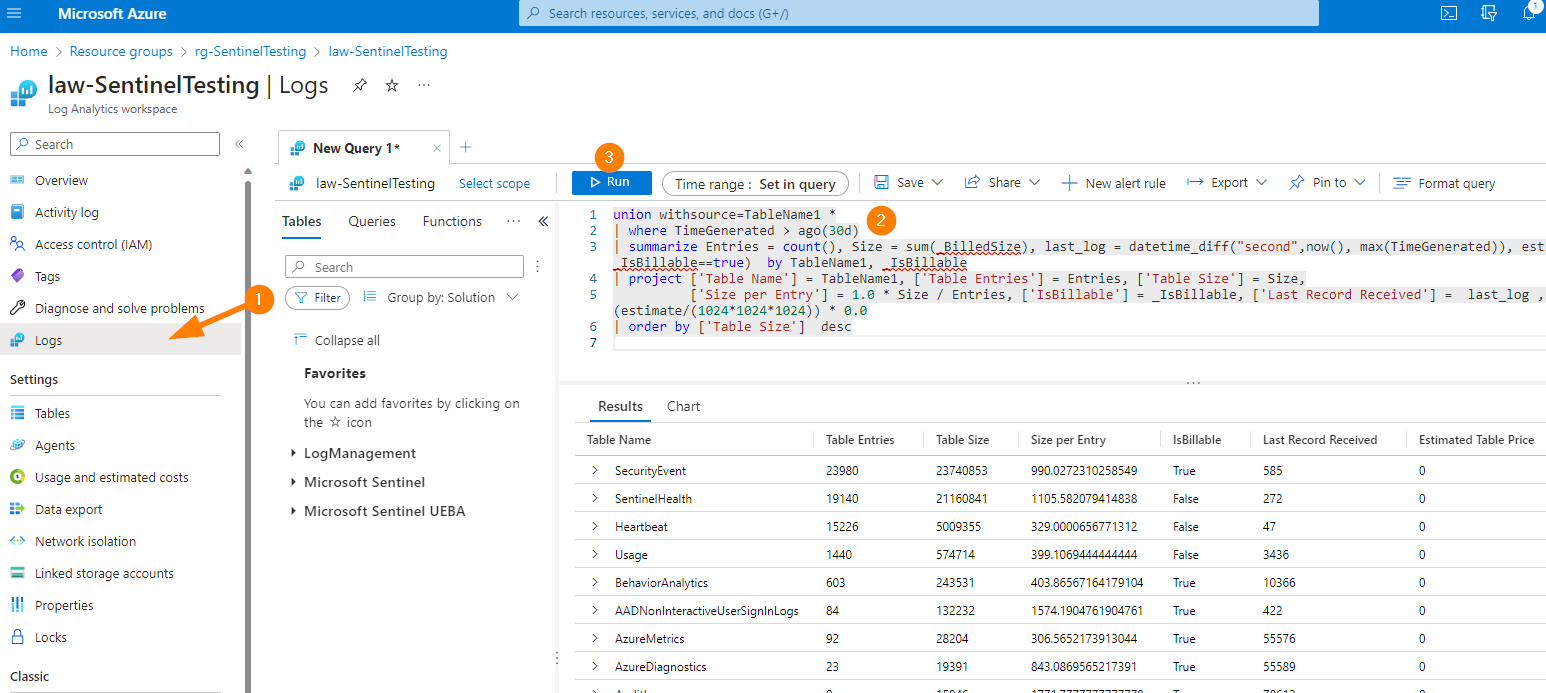
Cost Management & Microsoft Sentinel
Let’s talk about Microsoft Sentinel and managing costs. With cost being foundational pillar of Microsoft’s Well Architected Framework, part of good governance, and a major driver for product selection of SIEMs; let’s see if we can take some of mystery out of how to get started with managing costs in our favourite SIEM solution!
-
Where to find Incident Investigation Artifacts in M365
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Microsoft Defender tools are capable of collecting a lot of data, and that can create questions during investigations of where is all this data and how do I find it quickly? Join me for…
-
The Mysteries of Log Analytics Workspaces
Log Analytics workspaces provide a special way to store log data from multiple sources such as Microsoft Defender for Cloud, Azure Monitor, and so much more. A workspace typically combines data from multiple services and likely has it’s own distinct configuration for retention. I get a lot of questions about what the differences between workspaces…