defender
-

Reducing Risk with Attack Surface Reduction Rules
Many modern attacks don’t rely on exotic malware—they abuse normal application behavior. Office macros spawning PowerShell, scripts launching from temporary folders, or executables delivered through email are all techniques attackers use because they blend in with legitimate activity. Attack Surface Reduction (ASR) rules are designed to stop these behaviors before they turn into a breach.…
-
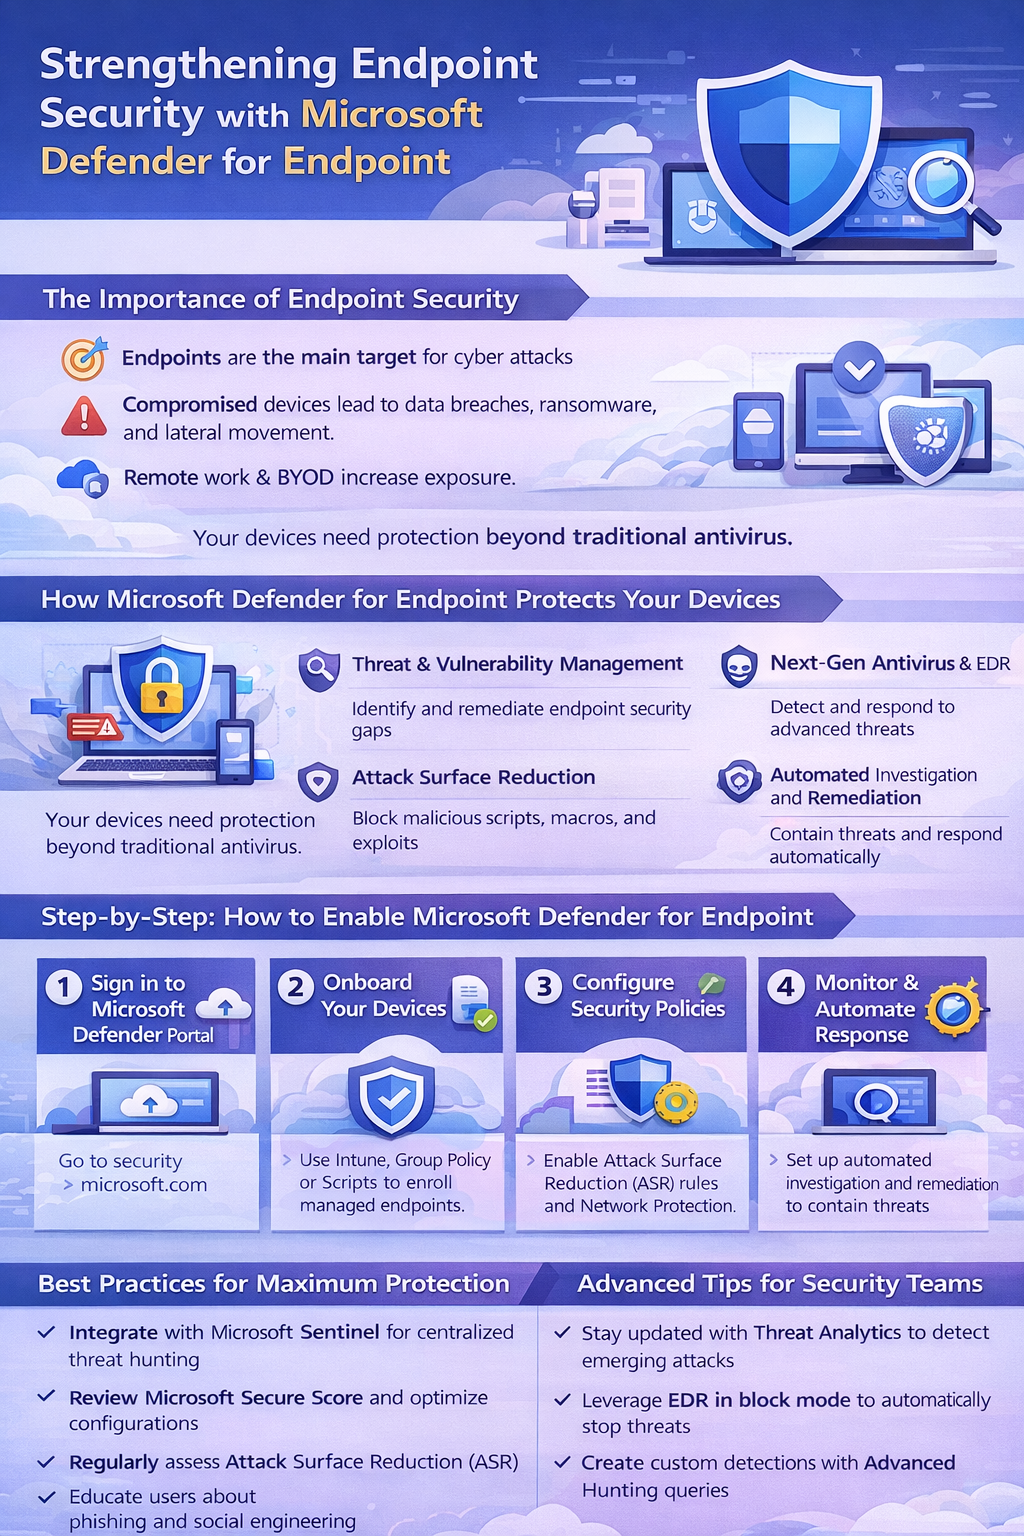
Strengthening Endpoint Security with Microsoft Defender for Endpoint
You will quickly discover that endpoints are the frontline of modern cyber defense — and the first targets for attackers. Laptops, desktops, servers, and mobile devices sit at the intersection of users, data, and the cloud, making them prime entry points for ransomware, credential theft, and lateral movement. This article explains how Microsoft Defender for…
-
Azure Updates – Number 126, November 19, 2025
Azure News Technical Update — a special Microsoft Ignite Edition! This summary delivers a focused snapshot of recent developments across Microsoft’s cloud and security ecosystem. It highlights key announcements, technical articles, and feature releases related to Azure, Architecture, Compute, and Security, including updates from Microsoft Sentinel and Defender XDR. The goal is to provide a…
-
Azure Updates – Number 116 – July 14, 2025
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Zero Trust with Microsoft Security Solutions: An Overview
In today’s rapidly evolving threat landscape, the traditional perimeter-based security model is no longer sufficient. As organizations adopt hybrid work environments, expand to the cloud, and connect countless devices, the attack surface grows exponentially. A “Zero Trust” security model offers a modern, proactive approach by assuming that no entity—whether inside or outside your network—can be…
-
Onboard a Single Subscription with Microsoft Defender for Cloud
In today’s post we will look at a targeted way to harness the full potential of your Azure security by integrating Microsoft Defender for Cloud with Microsoft Sentinel. This powerful combination allows for advanced threat detection, seamless monitoring, and a unified view of your security posture. We want to select our Sentinel data connectors while…
-
Defender for Cloud Cost Controls
Finding the true cost of cloud SaaS tooling is a complicated and elusive task. Microsoft has some different tools we can use to try and estimate costs that we’ll cover in this post. There are challenges in accurately estimating cloud consumption and usage costs due to day-to-day variances in that usage and other factors. Let’s…
-
Azure Updates – Number 70 – August 12, 2023
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes.
-
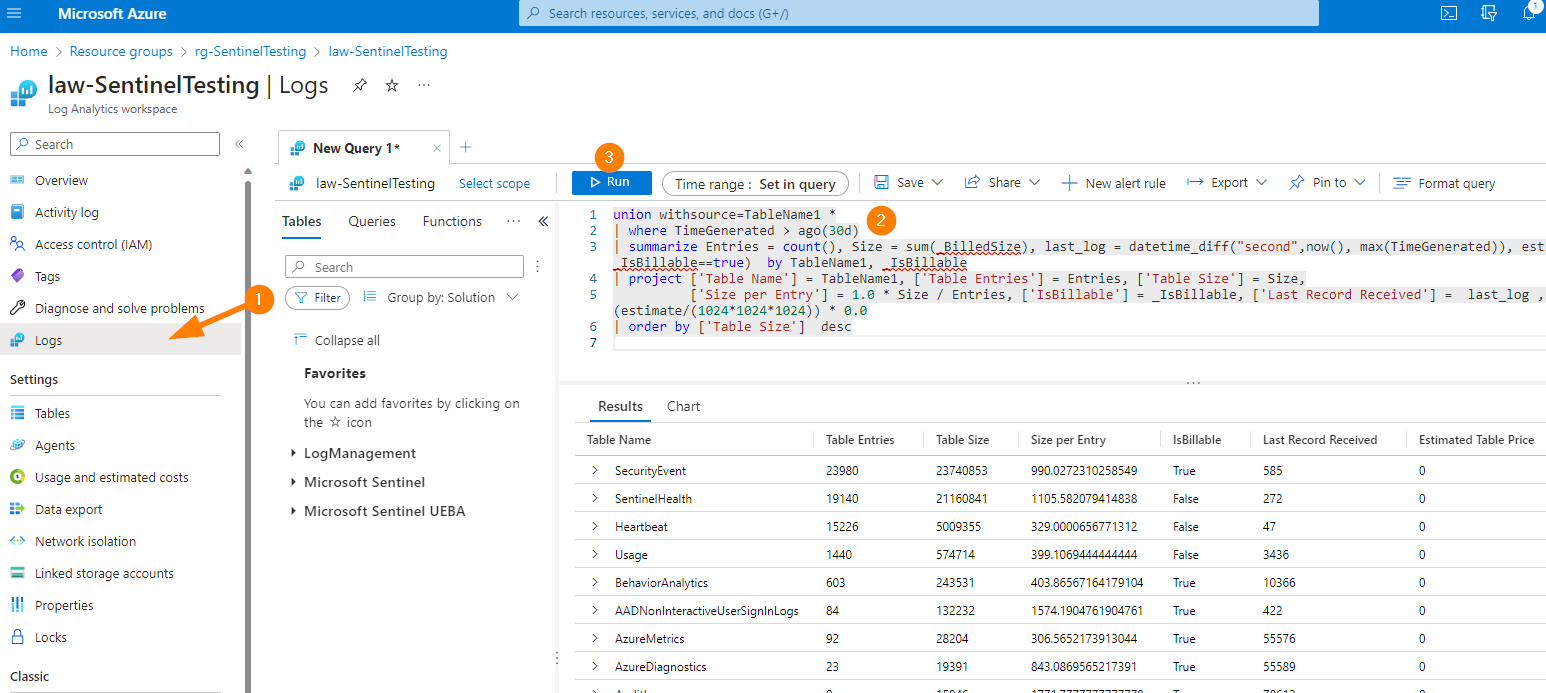
Responding to Incidents in Microsoft Sentinel
Join me to explore next steps once you have investigated an incident. Taking action to respond to the threat in Microsoft Sentinel provides excellent automated response capabilities that can be used to respond to threats in real-time. Let’s explore!
-
Where to find Incident Investigation Artifacts in M365 – Part 2 – The Portals
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Let’s explore the different portals where we can quickly explore our data and perform investigations…