Monitoring
-
Reduce Log Analytics Noise with Azure Monitor DCR Transformations
Security logging is only useful when the right data lands in the right place at a cost the organization can sustain. Noisy logs can hide real signals, inflate ingestion, and make analysts distrust the workspace. In this walkthrough, we build a controlled Data Collection Rule transformation, test the KQL logic, validate the resulting records in…
-
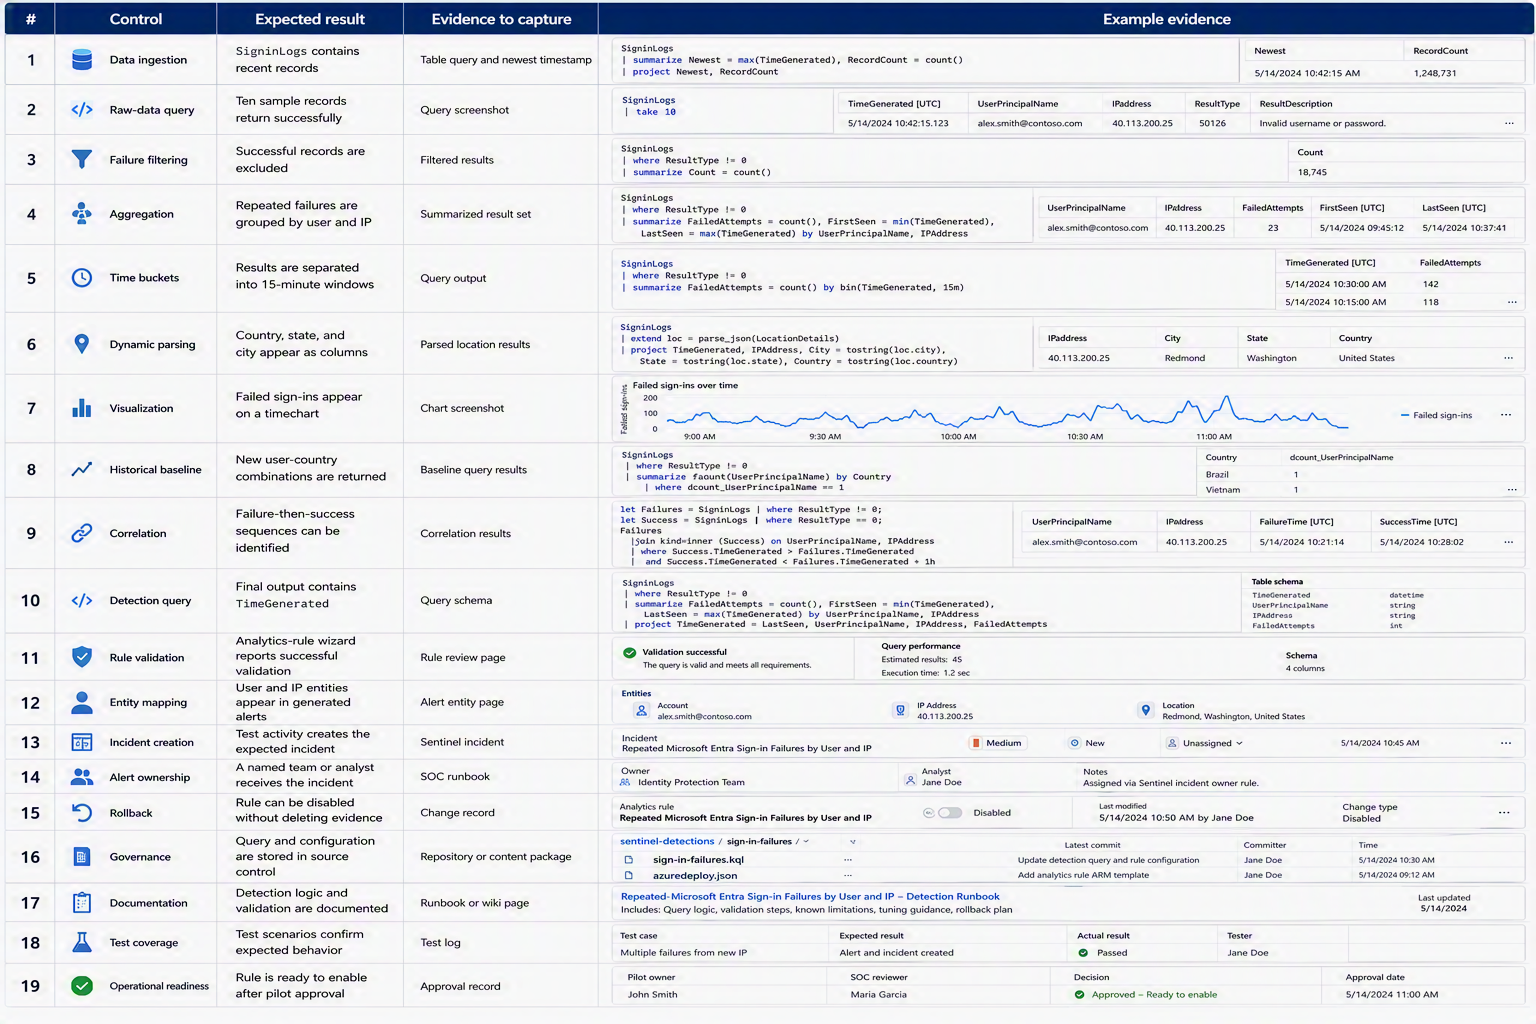
Saturday Heat – Bonus Walkthrough!
There is too much heat this week for me. I took the opportunity to try & find some distraction for you too! In this Saturday bonus article, we will build several practical security queries progressively. We will begin by reviewing raw Microsoft Entra sign-in data, add filters, summarize the results, extract values from dynamic fields,…
-

Responding to Ransomware with Azure’s Security Tools
Best practices for defending against ransomware with Microsoft’s security capabilities Ransomware isn’t just malware—it’s a breach. And in today’s threat landscape, it’s often human-operated, coordinated, and devastating. Microsoft Azure offers a layered defense strategy that combines proactive detection, rapid response, and resilient recovery. This article explores how to leverage Azure’s native security tools to build…
-
Microsoft Defender for Cloud: Deep Dive
In today’s cloud-first world, security isn’t just a checkbox—it’s a continuous discipline. Microsoft Defender for Cloud is the cornerstone of Azure’s native security posture management and threat protection. Whether you’re running workloads in Azure, AWS, GCP, or on-premises via Azure Arc, Defender for Cloud provides unified visibility, intelligent recommendations, and active threat detection.
-
Part 2: Visualizing DDoS Defense—Workbooks, Mitigation Reports & GitHub Tooling
Today we start the second phase of our DDoS protection journey—where visibility becomes your superpower, and raw telemetry transforms into strategic insight. You’ve done the hard work: diagnostic logging is enabled, your DDoS protection plan is active, and telemetry is flowing into Log Analytics. Now it’s time to elevate your defense posture from reactive to…
-
Building the Foundations of Azure DDoS Defense
Today we start a journey into the heart of Azure’s DDoS protection capabilities—not just to check a box, but to build a resilient, observable, and defensible cloud perimeter. DDoS attacks are no longer rare anomalies. They’re persistent, evolving threats that target everything from public-facing APIs to mission-critical web apps; and while Azure offers built-in protection,…
-
Monitoring and Analytics with Azure Monitor
In modern cloud environments, maintaining the health and performance of applications is critical. Azure Monitor provides a full-stack monitoring solution that enables organizations to track metrics, diagnose issues, and gain deep insights into their applications and infrastructure. Whether monitoring virtual machines (VMs), Kubernetes clusters, databases, or application services, Azure Monitor ensures optimal performance with proactive…
-
Onboard a Single Subscription with Microsoft Defender for Cloud
In today’s post we will look at a targeted way to harness the full potential of your Azure security by integrating Microsoft Defender for Cloud with Microsoft Sentinel. This powerful combination allows for advanced threat detection, seamless monitoring, and a unified view of your security posture. We want to select our Sentinel data connectors while…
-
Monitor Sentinel Data Connector Health – Alerting
Join me in taking a look at exploring Sentinel health data and using KQL to create an alert rule that tells our SOC team about data connector issues in Sentinel. This post walks through the KQL queries, exploring your data, and creating an alerting rule. Monitoring is an important part of good governance in Sentinel!
-
Monitor Sentinel Data Connector Health
There is more than one way to monitor most Azure infrastructure and data connectors are no exception. Today we look at creating a way to keep an eye on your data connectors operations in Sentinel, using Sentinel. Join me for a few minutes as we explore one of the important best practices in Microsoft Sentinel…