KQL
-
Reduce Log Analytics Noise with Azure Monitor DCR Transformations
Security logging is only useful when the right data lands in the right place at a cost the organization can sustain. Noisy logs can hide real signals, inflate ingestion, and make analysts distrust the workspace. In this walkthrough, we build a controlled Data Collection Rule transformation, test the KQL logic, validate the resulting records in…
-
Thunderstruck in Microsoft Defender XDR
This article builds a controlled Microsoft Defender XDR hunt that correlates process and network telemetry, creates a reusable filtered data set, assigns a transparent risk score, and identifies unusual scripting volume. The AC/DC theme stays light; the technical work does not. Bringing a couple of my own passions for metal & KQL together! Join me…
-
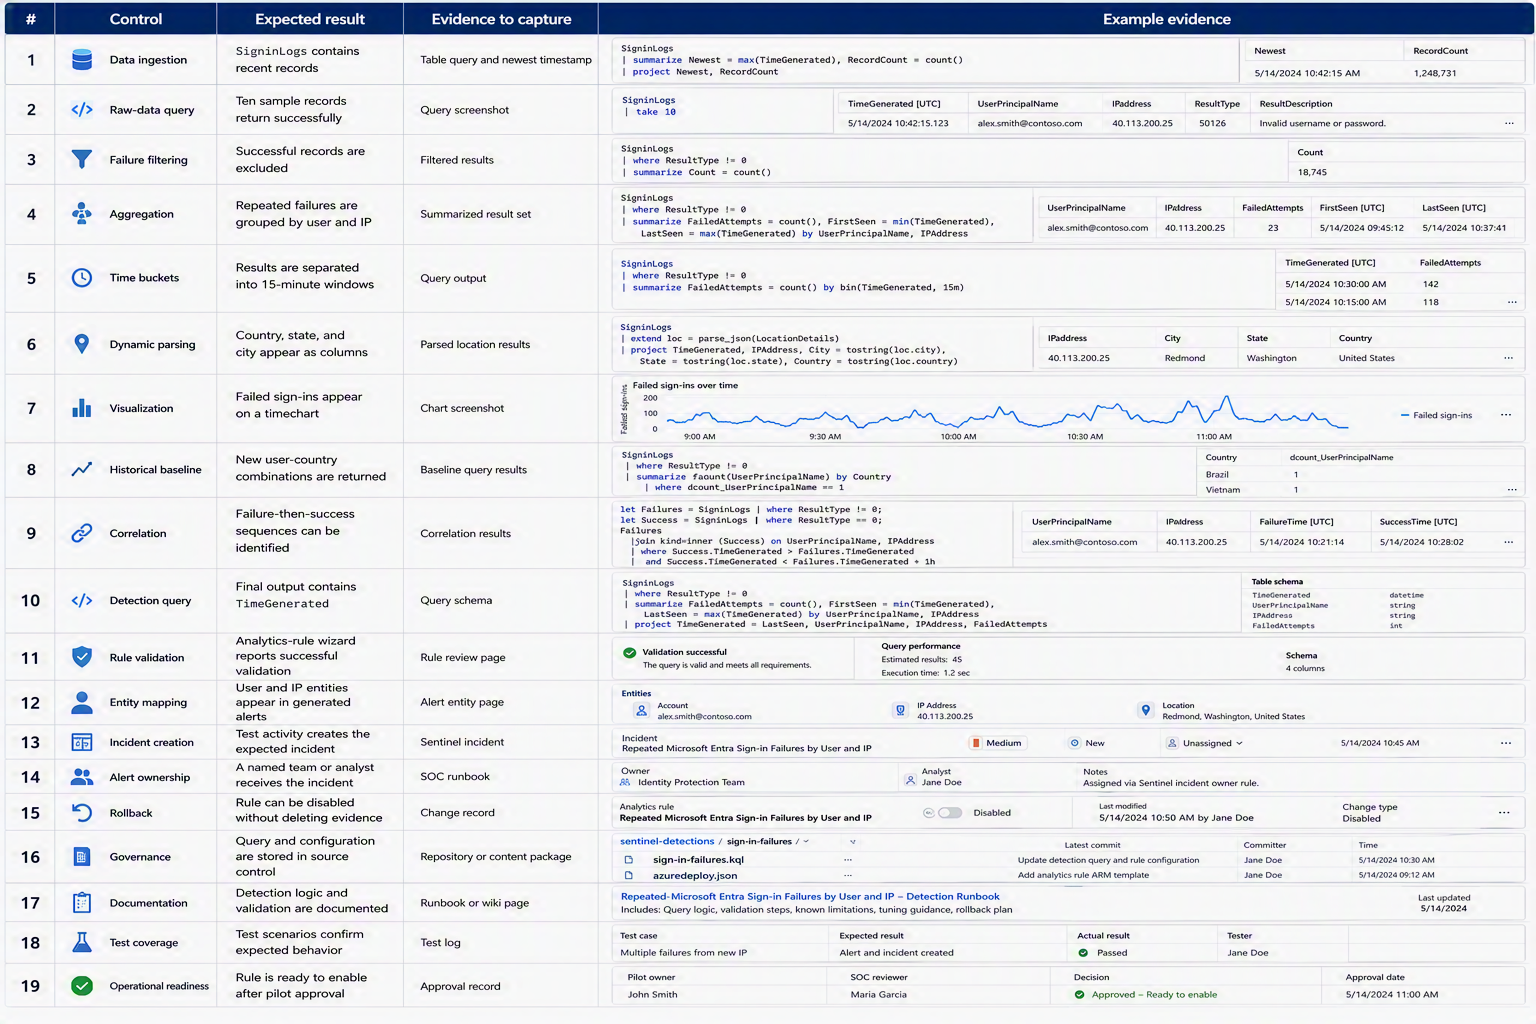
Saturday Heat – Bonus Walkthrough!
There is too much heat this week for me. I took the opportunity to try & find some distraction for you too! In this Saturday bonus article, we will build several practical security queries progressively. We will begin by reviewing raw Microsoft Entra sign-in data, add filters, summarize the results, extract values from dynamic fields,…
-

Querying Logic App Performance with KQL: A Practical Guide
This post explores how to query Logic App performance using Kusto Query Language (KQL), with a focus on measuring workflow run durations. It breaks down telemetry sources based on Logic App type—Consumption vs. Standard—and guides readers through using AzureDiagnostics, Traces, and LogicAppWorkflowRuntime tables. The article includes practical KQL examples for schema discovery, execution tracking, and…
-
How do I Start Threat Hunting with Microsoft Sentinel?
Join me as I explore getting started with threat hunting using Microsoft Sentinel and KQL to jump-start our investigations. We will dive into a world where we look for anomalies in the data and try to identify potential threats before they can escalate within our environment.
-
Using KQL with Azure Arc Machine Status
In this post we take a look at using KQL to observe machine status of Azure Arc managed machines. We will look at a couple of examples of how to create some helpful queries and then using those to enable monitoring in Microsoft Sentinel. As organizations adopt a more cloud-centric management model, it is becoming…
-
Find Failed Create Operations in Azure using KQL
Today, we embark on a thrilling quest through the Azure cosmos to uncover the secrets of failed create operations using Kusto Query Language (KQL). This quick post will equip you with the knowledge to track down those elusive “create” mishaps and help find clues behind these operations quickly.
-
Unveil Delete Operations in Azure using KQL
In this blog post, we’ll explore how to wield the mighty KQL to uncover those elusive “delete” actions within your Azure environment. Whether you’re a seasoned cloud explorer or just dipping your toes into the Azure waters, this guide will equip you with the knowledge to track down those vanishing resources.
-
Find Actions Taken by an Administrator in Azure Logs
In this post, join me in exploring how to find meaningful actions taken by an administrator in your environment. We will take a look at how to find what changes were made by an individual account. Join me as we dive into auditing logs in Azure and determine if the administrator account is responsible for…