automation
-
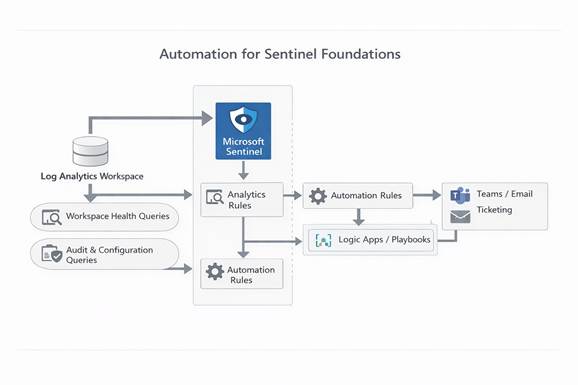
Microsoft Sentinel Baseline Deployment: From Zero to Operational SOC – Summer Bonus!
Microsoft Sentinel is powerful—but it can’t manage itself. Manual operations like onboarding data connectors, validating ingestion, monitoring workspace health, and auditing configuration changes quickly become a burden. This bonus article walks through building automation around your Sentinel foundations, so you can: Keep your workspaces healthy Ensure configuration compliance Alert on critical changes Free SOC engineers…
-
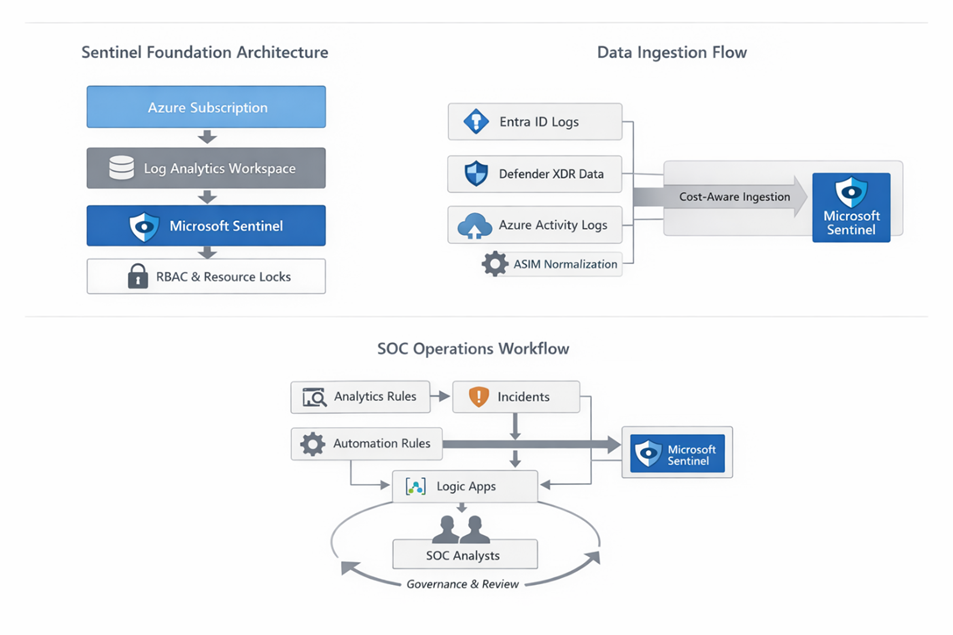
Microsoft Sentinel Baseline Deployment: From Zero to Operational SOC – Part 3 of 3
Sentinel does not fail because it lacks detections. It fails because alerts overwhelm analysts, automation hides context, and governance is treated as an afterthought. In this series-finale post, we establish a production operational baseline: analytics rules, incident handling, automation boundaries, and long-term governance. This is where Sentinel becomes usable—not just enabled. There is no secret…
-

Microsoft Defender for Cloud Use Case: Governance Rules in Action
Security at scale isn’t just about visibility—it’s about enforcement. As organizations grow their cloud footprint across multiple subscriptions, management groups, and even cloud providers, maintaining consistent security posture becomes exponentially harder. Enter Governance Rules in Microsoft Defender for Cloud (MDC). These rules allow security teams to define, enforce, and monitor security policies across their environment…
-
Microsoft Defender for Cloud: Deep Dive
In today’s cloud-first world, security isn’t just a checkbox—it’s a continuous discipline. Microsoft Defender for Cloud is the cornerstone of Azure’s native security posture management and threat protection. Whether you’re running workloads in Azure, AWS, GCP, or on-premises via Azure Arc, Defender for Cloud provides unified visibility, intelligent recommendations, and active threat detection.
-

Top Azure Services for Supporting Small Businesses
In today’s digital-first world, small businesses must leverage cost-effective, scalable, and secure cloud solutions to stay competitive. Microsoft Azure offers a powerful ecosystem of cloud services that can help businesses improve efficiency, security, and innovation without requiring extensive technical expertise. One of the biggest advantages of Azure and Microsoft Cloud is the ability to toggle…
-
Automated Triage in Microsoft Sentinel
In today’s post we will look at some different ways to automate incident triage in Microsoft Sentinel. Organizations face an ever-increasing volume of security threats. Cyberattacks are becoming more sophisticated, and the sheer number of alerts can overwhelm even the most seasoned security teams. Automated triage in Microsoft Sentinel emerges as a crucial solution, empowering…
-
Azure Updates – Number 99 – October 5, 2024
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Enhancing Microsoft Sentinel: Part 3 – Ongoing Optimization and Staying Ahead of Threats
Join me for the final article in the min-series on Enhancing Microsoft Sentinel. Today, we review ongoing optimizations and how to stay ahead of emerging threats.
-
Enhancing Microsoft Sentinel: Part 2 – Advanced Customization and Threat Hunting
Join me for Part 2 of 3 where we review advanced customizations in Microsoft Sentinel. We review some of the steps to advance your threat hunting and better protect your environment.
-
Enhancing Microsoft Sentinel: Part 1 – Building a Stronger Foundation
Join me for Part 1 of 3 where we review Building a Stronger Foundation in Microsoft Sentinel. We review the steps to help review and build a stronger SIEM solution together.