Azure
-

Azure Updates – Number 144 – August 22, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Thunderstruck in Microsoft Defender XDR
This article builds a controlled Microsoft Defender XDR hunt that correlates process and network telemetry, creates a reusable filtered data set, assigns a transparent risk score, and identifies unusual scripting volume. The AC/DC theme stays light; the technical work does not. Bringing a couple of my own passions for metal & KQL together! Join me…
-
Azure Updates – Number 143 – August 8, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
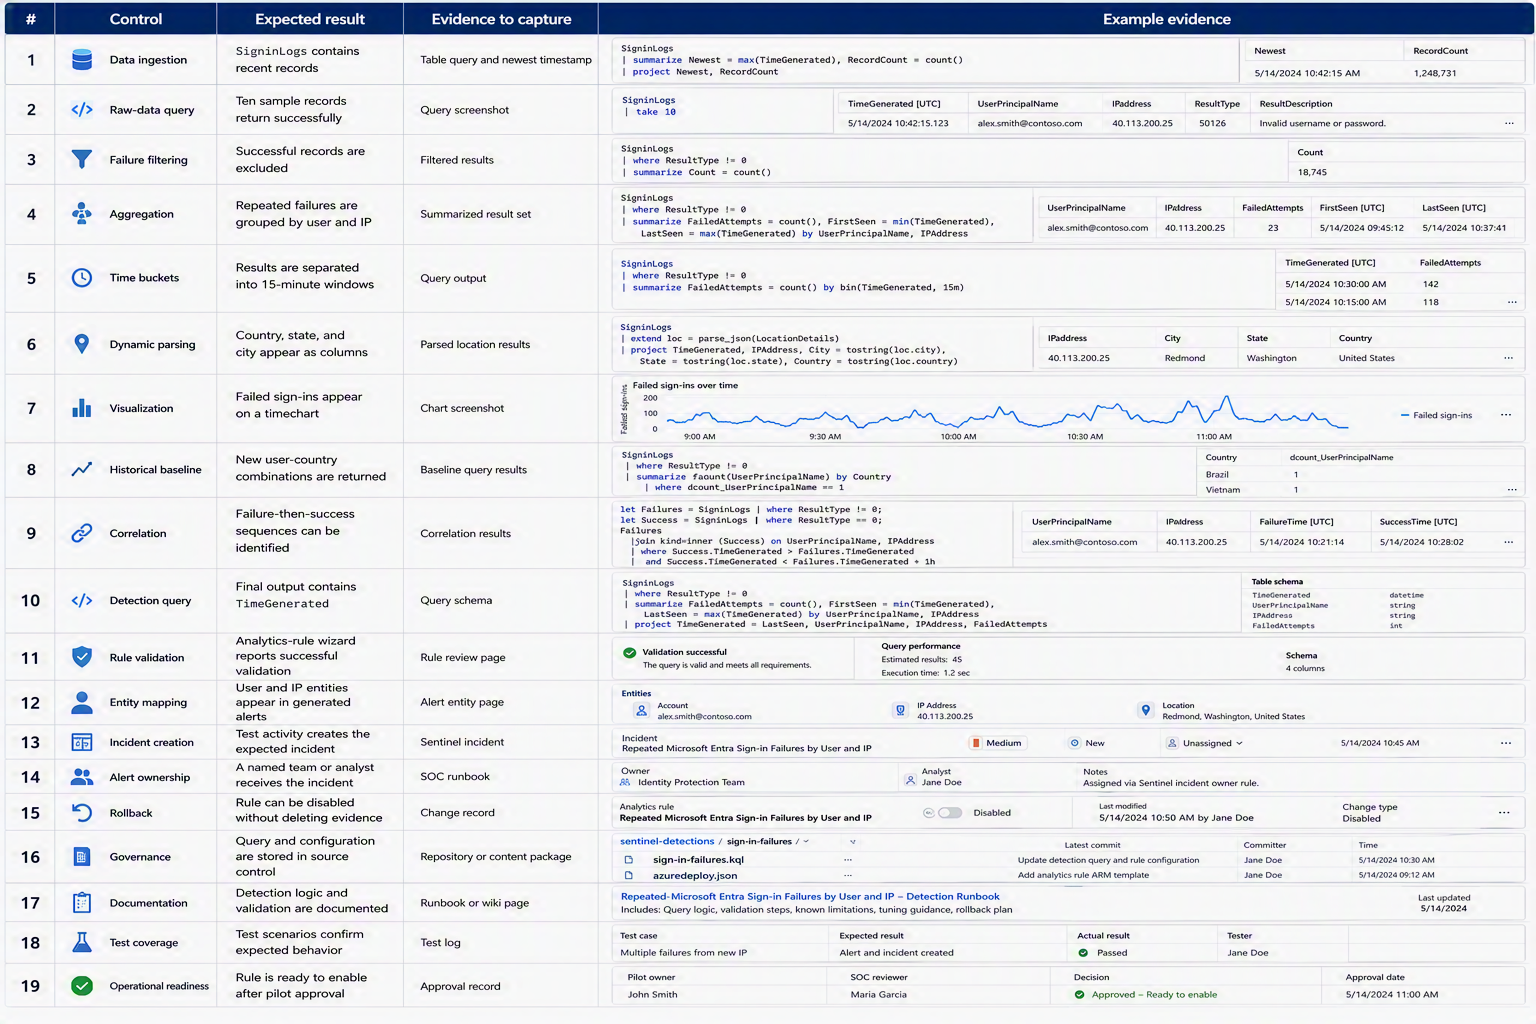
Saturday Heat – Bonus Walkthrough!
There is too much heat this week for me. I took the opportunity to try & find some distraction for you too! In this Saturday bonus article, we will build several practical security queries progressively. We will begin by reviewing raw Microsoft Entra sign-in data, add filters, summarize the results, extract values from dynamic fields,…
-
Azure Updates – Number 142 – July 25, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Azure Updates – Number 141 – July 11, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Azure Updates – Number 140 – June 27, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
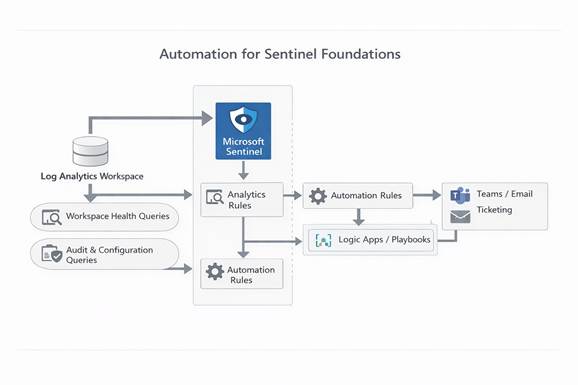
Microsoft Sentinel Baseline Deployment: From Zero to Operational SOC – Summer Bonus!
Microsoft Sentinel is powerful—but it can’t manage itself. Manual operations like onboarding data connectors, validating ingestion, monitoring workspace health, and auditing configuration changes quickly become a burden. This bonus article walks through building automation around your Sentinel foundations, so you can: Keep your workspaces healthy Ensure configuration compliance Alert on critical changes Free SOC engineers…
-
Azure Updates – Number 139 – June 13, 2026
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
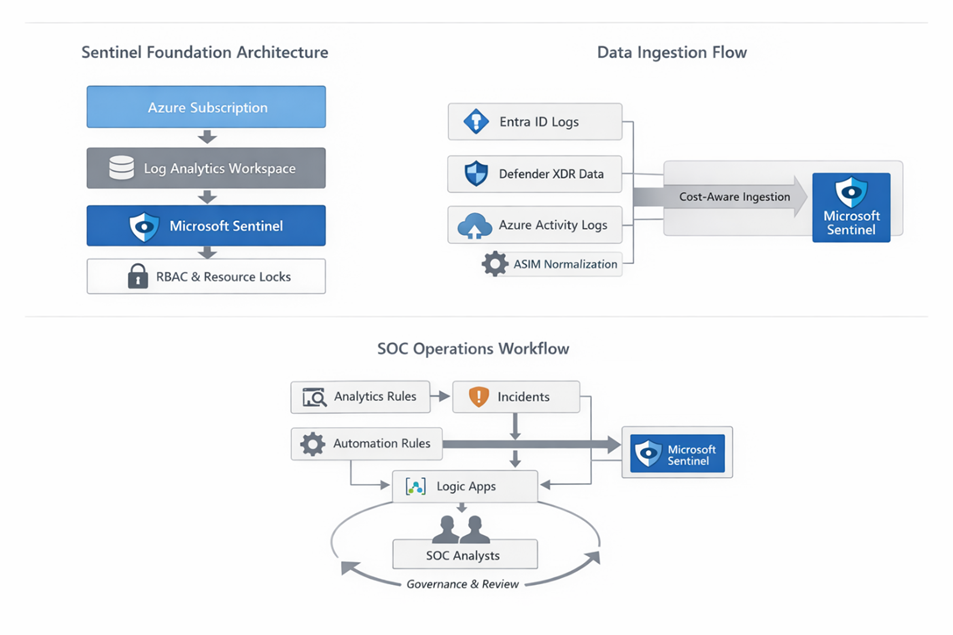
Microsoft Sentinel Baseline Deployment: From Zero to Operational SOC – Part 3 of 3
Sentinel does not fail because it lacks detections. It fails because alerts overwhelm analysts, automation hides context, and governance is treated as an afterthought. In this series-finale post, we establish a production operational baseline: analytics rules, incident handling, automation boundaries, and long-term governance. This is where Sentinel becomes usable—not just enabled. There is no secret…