Storage
-
Deploy Microsoft Defender for Storage with Malware Scanning and Sensitive Data Threat Detection
Azure Storage often becomes the handoff point for partners, applications, automation jobs, exports, and user-generated files. That makes it a high-value security boundary: a malicious upload, exposed blob container, or unusual access pattern can turn a simple storage account into an incident source.
-

Building Resilience with Azure Site Recovery
Business continuity is no longer optional — it is a core requirement for any organization operating in the cloud. Service outages, cyber incidents, and regional failures are not a question of if, but when. Azure Site Recovery (ASR) provides the foundation for a resilient, enterprise-grade disaster recovery strategy by enabling continuous replication, automated failover, and…
-

Future-Ready SOCs: Microsoft Sentinel Data Lake Powers AI-Driven Security
As 2025 wraps up, Microsoft Sentinel takes center stage with a major innovation announced at Ignite: Sentinel Data Lake. This feature is designed to unify security signals, reduce SIEM costs, and enable AI-powered threat detection at scale. In this article, we’ll explore what Sentinel Data Lake means for SOC operations, why it matters, and how…
-
Building a Microsoft Sentinel Data Use Case
Join me this week to gain an in-depth understanding on how to clearly define what data to retain. Data retention is not just a regulatory box to tick; it’s the backbone of a robust security posture. In the realm of Microsoft Sentinel, understanding how to manage your data retention is key to leveraging the full…
-
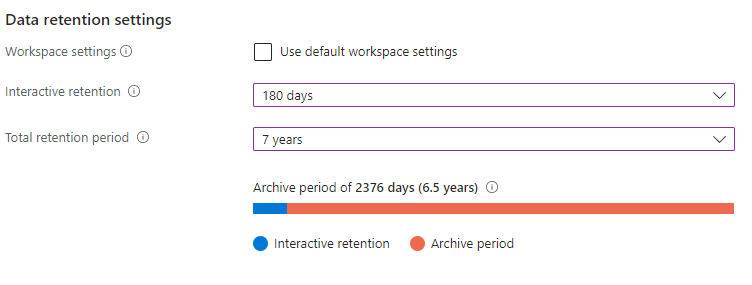
Cost Management & Microsoft Sentinel Part 2
Today we explore additional cost management options to use as part of your ongoing governance in Microsoft Sentinel. Let’s dive into the world of Log Analytics Workspace configurations together!
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 1
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 1 of How do I create incidents to test with?
-
Set Log Analytics Workspace Data Cap
Let’s take a look at setting data ingestion caps in an Azure Log Analytics workspace today. There are different reasons why we may want to limit the data coming into our storage account, today we look at both setting the data cap, and alerting us when that data cap is reached through Azure Monitor alerting.
-
Sentinel & Log Analytics – Where is my Data?
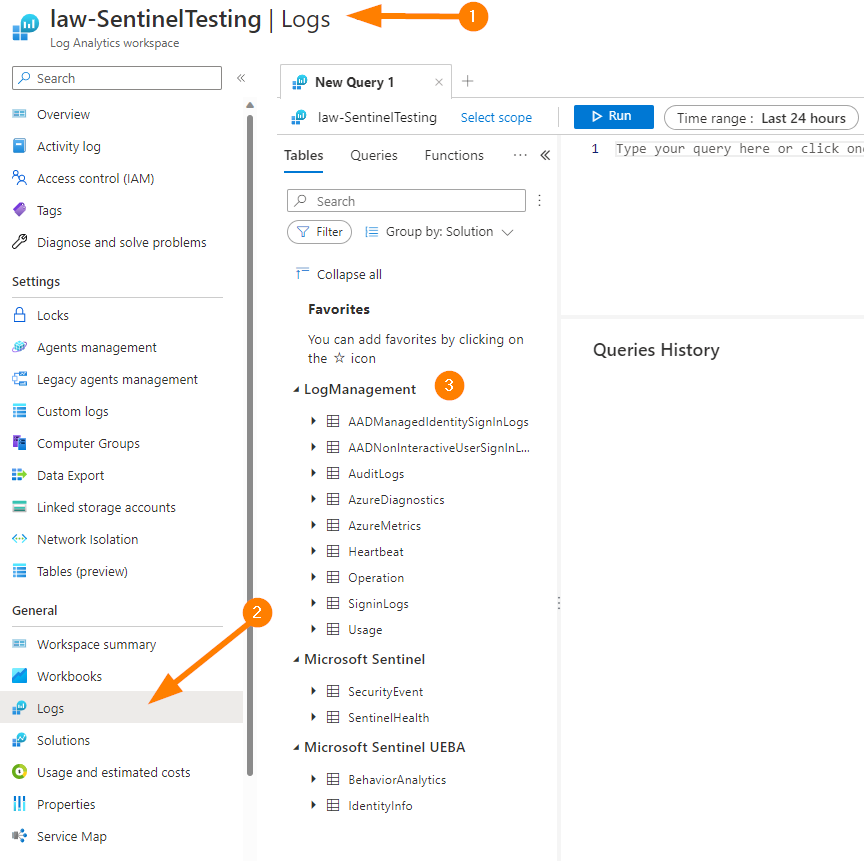
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Where is my Data?
-
Deploy a Log Analytics Workspace
A log analytics workspace is an environment that is made especially for storing log data. This can be Azure Monitor, or other diagnostic log data. We’ll cover a few different uses for log analytics data in this article and how to get data into your workspace. Know that each workspace has it’s own data repository,…
-
The Mysteries of Log Analytics Workspaces
Log Analytics workspaces provide a special way to store log data from multiple sources such as Microsoft Defender for Cloud, Azure Monitor, and so much more. A workspace typically combines data from multiple services and likely has it’s own distinct configuration for retention. I get a lot of questions about what the differences between workspaces…