soc
-
Saturday Heat – Bonus Walkthrough!
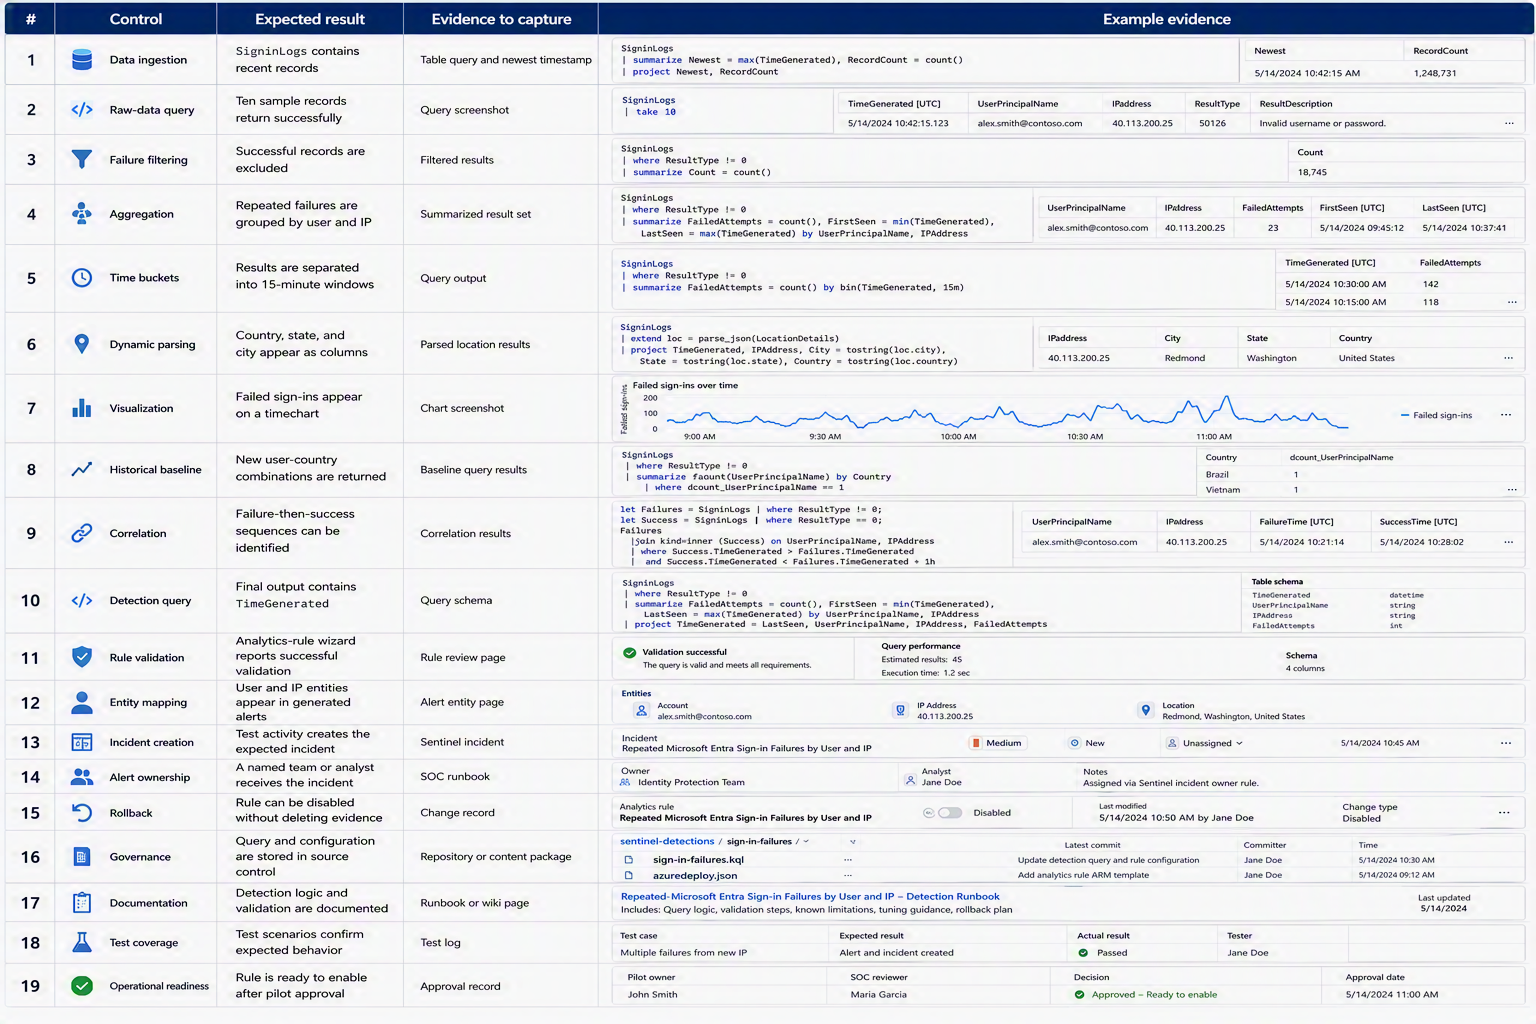
There is too much heat this week for me. I took the opportunity to try & find some distraction for you too! In this Saturday bonus article, we will build several practical security queries progressively. We will begin by reviewing raw Microsoft Entra sign-in data, add filters, summarize the results, extract values from dynamic fields,…
-
Azure Updates – Number 126, November 19, 2025
Azure News Technical Update — a special Microsoft Ignite Edition! This summary delivers a focused snapshot of recent developments across Microsoft’s cloud and security ecosystem. It highlights key announcements, technical articles, and feature releases related to Azure, Architecture, Compute, and Security, including updates from Microsoft Sentinel and Defender XDR. The goal is to provide a…
-
Azure Updates – Number 109 – March 8, 2025
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Azure Updates – Number 106 – January 11, 2025
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, Security Copilot and Sentinel topics. Save time digging around to find recent releases and changes.
-
Post High Severity Incidents in Sentinel to a Teams Channel
Today we explore incident communication using Teams. One of the great things about Microsoft Sentinel is the ability to integrate with Microsoft Teams, allowing for seamless collaboration and communication during high-severity incident responses. We will take a look at getting Teams working using a step-by-step guide to post summary information from incidents directly to a…
-
Find Failed Create Operations in Azure using KQL
Today, we embark on a thrilling quest through the Azure cosmos to uncover the secrets of failed create operations using Kusto Query Language (KQL). This quick post will equip you with the knowledge to track down those elusive “create” mishaps and help find clues behind these operations quickly.
-
Unveil Delete Operations in Azure using KQL
In this blog post, we’ll explore how to wield the mighty KQL to uncover those elusive “delete” actions within your Azure environment. Whether you’re a seasoned cloud explorer or just dipping your toes into the Azure waters, this guide will equip you with the knowledge to track down those vanishing resources.
-
Incident Response Foundations – Identity
In today’s post I talk about responding to a compromised identity in Microsoft Entra ID. There is a lot of advice floating around on what to do and how to respond; I’m bringing experiences and existing guidelines together to provide a solid foundational starting point for identity based incident response in this post.
-
Responding to Incidents with Microsoft Sentinel – Part 5 – Take Action with Automation
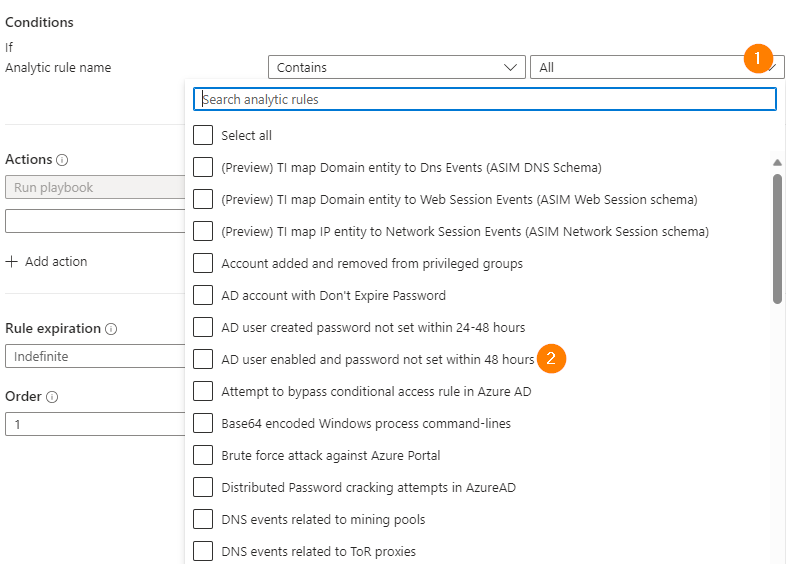
In today’s article we will build on previous automation experiences to further develop your Microsoft Sentinel automation powers! Today we will look at remediating incidents and alerts automatically. We will explore auto-remediation using both playbooks and Sentinel Automation rules.
-
Responding to Incidents with Microsoft Sentinel – Part 4 – Automate Research
Today we take a detailed look at building our own Sentinel Playbooks and gathering information on an Incident automatically. Join me as we build automation to update Alerts with detailed IP lookup information as comments. With basic research done automatically, we can save a lot of time!