Security
-
Azure Updates – Number 54 – December 31, 2022
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes.
-
Sentinel Health Data Visualization & Reporting
A common challenge after deploying Microsoft Sentinel has been how to keep track of your Data Connector health status. Last article, we explored getting a handle on our Microsoft Sentinel data connectors health. This week, we look visualizing and using that data with Sentinel Workbooks.
-
Sentinel Data Connector Health Monitoring
A common challenge after deploying Microsoft Sentinel has been how to keep track of Data Connectors health. Today, we take a look at getting a handle on how to start monitoring our Microsoft Sentinel data connectors health.
-
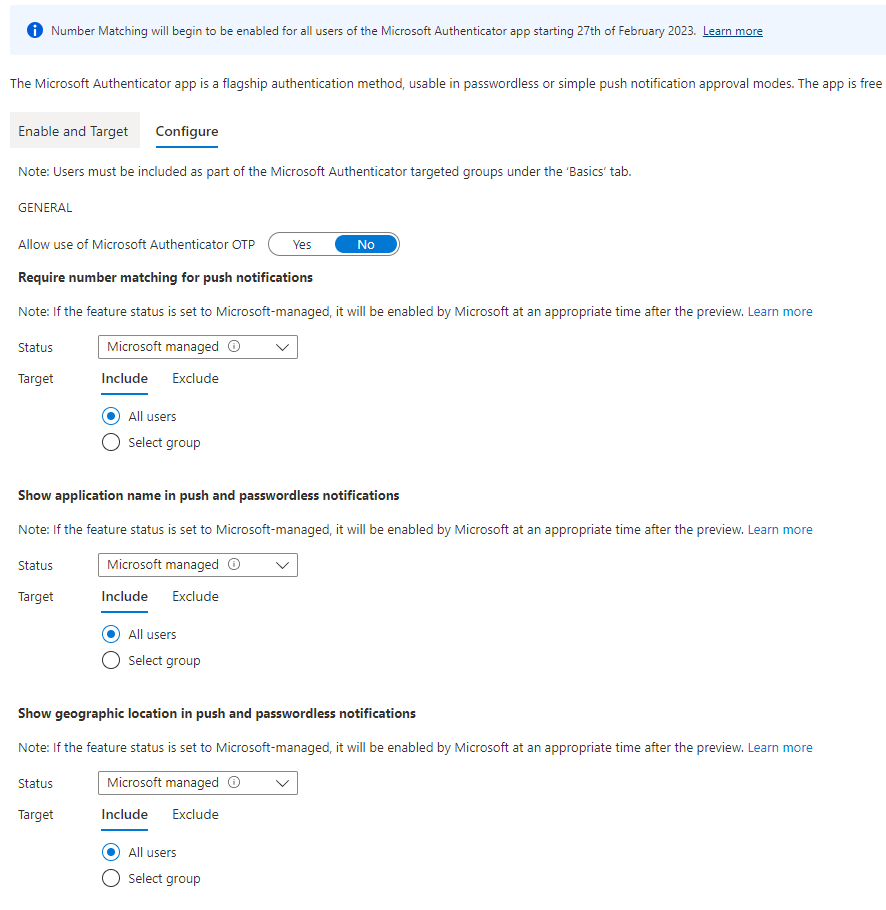
Modernize your Microsoft Authenticator Policies
Getting ready to move into Azure Active Directory or make changes to your Microsoft Entra configurations? The last few weeks I’ve talked about MFA and conditional access rules; so this week we will look at the preview for Microsoft Authenticator Policies, then change gears and talk about how to get our users excited about these…
-
Migrate Azure Multi-Factor Authentication Server to cloud-based Azure MFA
With the end of support for Azure MFA server on-premises coming soon, it’s time to start planning the move to Azure cloud-based MFA. Let’s look at the steps to starting our migration to Azure AD MFA.
-
Where to find Incident Investigation Artifacts in M365 – Part 2 – The Portals
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Let’s explore the different portals where we can quickly explore our data and perform investigations…
-
Where to find Incident Investigation Artifacts in M365
A common challenge that security teams face is simply not knowing where all the artifacts can be found during an investigation. Microsoft Defender tools are capable of collecting a lot of data, and that can create questions during investigations of where is all this data and how do I find it quickly? Join me for…
-
M365 Operating Guide for Sec Ops Teams – Use with Microsoft Sentinel
When building out a SOC team, many organizations quickly realize that there are very few silos left in IT when it comes to cloud. Our SOC members need to have cloud platform skills, M365, Exchange, Active Directory, Azure Active Directory, Windows Server, REHL, and so many more skills. To say this a different way; our…
-

Azure Updates – Number 38 – May 27, 2022 – Microsoft Build Edition
A special out of band update edition to cover the great updates released May 27, 2022 at the conclusion of Microsoft Build. Check out all the developer centric, Azure infrastructure, and Azure service updates in this special update!
-
The Mysteries of Log Analytics Workspaces
Log Analytics workspaces provide a special way to store log data from multiple sources such as Microsoft Defender for Cloud, Azure Monitor, and so much more. A workspace typically combines data from multiple services and likely has it’s own distinct configuration for retention. I get a lot of questions about what the differences between workspaces…