Security
-
Strengthening Cyber Defenses Against Modern Threats
In today’s digital age, cyber threats have evolved into sophisticated attacks that exploit vulnerabilities on an unprecedented scale. It’s crucial to understand these threats and take proactive steps to protect your organization. In this article, we explore the evolving landscape of cybercrime and provide actionable measures to safeguard your digital assets. Today, we continue our…
-
Strengthening Cybersecurity: Protecting Against 99% of Attacks
In the ever-evolving landscape of cybersecurity, one undeniable truth stands out—implementing fundamental security hygiene practices can thwart the vast majority of cyberattacks. By adhering to these minimum-security standards, it is possible to protect against over 99 percent of attacks. In this article, we’ll delve into these essential practices and explore how they can fortify your…
-

Strengthening Cybersecurity: The Power of Collective Defense
Cybersecurity stands as one of the paramount challenges facing organizations worldwide. The relentless evolution of cyber threats demands constant vigilance and adaptation. Microsoft, with its unique vantage point in the field, offers valuable insights into this ever-changing landscape to us through their Digital Defense Report. Today, I walk through some top highlights from that report…
-
Advanced Customization of Microsoft Sentinel Analytics Rules
Join me as we walk through creating a custom Microsoft Sentinel Analytics Rule using KQL to identify suspicious login patterns based on failed attempts. We will explore the different components of creating these custom rules, what tuning looks like, and creating incidents from the rules.
-
Responding to Incidents with Microsoft Sentinel – Part 4 – Automate Research
Today we take a detailed look at building our own Sentinel Playbooks and gathering information on an Incident automatically. Join me as we build automation to update Alerts with detailed IP lookup information as comments. With basic research done automatically, we can save a lot of time!
-
Responding to Incidents with Microsoft Sentinel – Part 2 – Optimize What You See
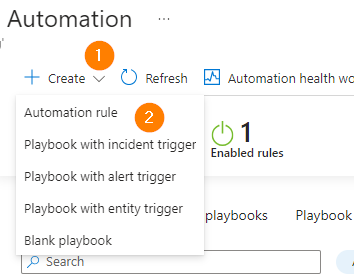
Today, we will explore some enhancements to your Microsoft Sentinel environment. I look at optimizing the ticket queue and working to prevent ticket overload. Join me to explore Automation Rules.
-
Responding to Incidents in Microsoft Sentinel
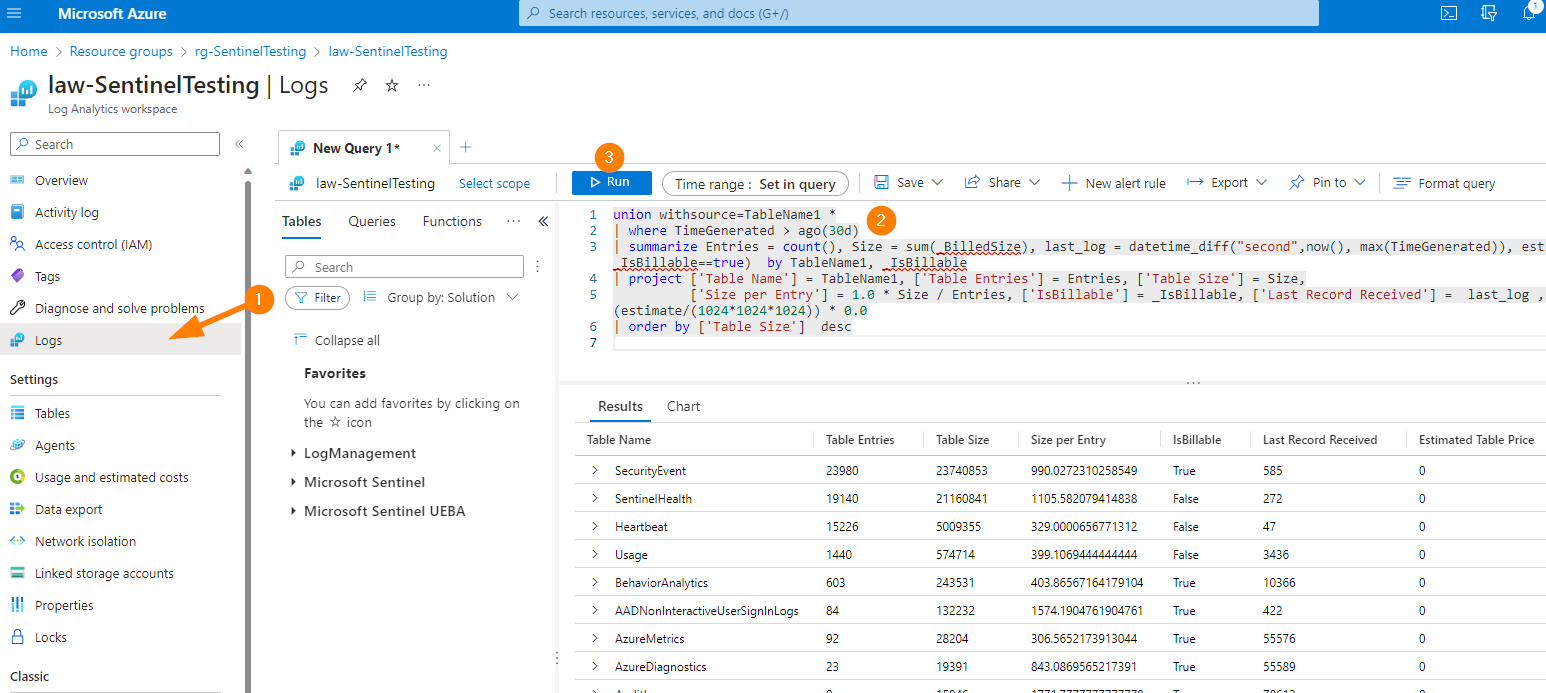
Join me to explore next steps once you have investigated an incident. Taking action to respond to the threat in Microsoft Sentinel provides excellent automated response capabilities that can be used to respond to threats in real-time. Let’s explore!
-
Responding to Threats with Microsoft Sentinel
Knowing where to start with Sentinel Incidents speeds remediation and supports making better decisions. Today, let’s take a look at monitoring and responding to cyber threats using Microsoft Sentinel.
-
Building Automation Rules with your Sentinel Instance in PowerShell
Today, we explore creating custom Automation Rules in Microsoft Sentinel to help us auto-close low value incidents. Let’s look at how we can automatically close & impact incidents and make it all work using PowerShell!
-
How to Build Custom Microsoft Sentinel Analytics Rules
Today, we expand on and explore rapid Microsoft Sentinel deployment using PowerShell. This model of repeatable, consistent, and fast deployments is a great way to help build our own skills up, and build a resilient and robust deployment method we can count on.