Security
-
Unveil Delete Operations in Azure using KQL
In this blog post, we’ll explore how to wield the mighty KQL to uncover those elusive “delete” actions within your Azure environment. Whether you’re a seasoned cloud explorer or just dipping your toes into the Azure waters, this guide will equip you with the knowledge to track down those vanishing resources.
-
Defender for Cloud Cost Controls
Finding the true cost of cloud SaaS tooling is a complicated and elusive task. Microsoft has some different tools we can use to try and estimate costs that we’ll cover in this post. There are challenges in accurately estimating cloud consumption and usage costs due to day-to-day variances in that usage and other factors. Let’s…
-
Fortifying Your Cyber Defenses: Preventing Unmanaged Device Compromises
In the evolving landscape of cyber threats, ransomware operators are increasingly targeting unmanaged devices. These devices, including personal devices used for work-related tasks, often lack the robust security measures found in managed systems. Understanding these evolving threats and taking proactive steps to protect your organization is paramount. Today, our article delves into the challenges posed…
-
Strengthening Cyber Defenses Against Modern Threats
In today’s digital age, cyber threats have evolved into sophisticated attacks that exploit vulnerabilities on an unprecedented scale. It’s crucial to understand these threats and take proactive steps to protect your organization. In this article, we explore the evolving landscape of cybercrime and provide actionable measures to safeguard your digital assets. Today, we continue our…
-
Strengthening Cybersecurity: Protecting Against 99% of Attacks
In the ever-evolving landscape of cybersecurity, one undeniable truth stands out—implementing fundamental security hygiene practices can thwart the vast majority of cyberattacks. By adhering to these minimum-security standards, it is possible to protect against over 99 percent of attacks. In this article, we’ll delve into these essential practices and explore how they can fortify your…
-

Strengthening Cybersecurity: The Power of Collective Defense
Cybersecurity stands as one of the paramount challenges facing organizations worldwide. The relentless evolution of cyber threats demands constant vigilance and adaptation. Microsoft, with its unique vantage point in the field, offers valuable insights into this ever-changing landscape to us through their Digital Defense Report. Today, I walk through some top highlights from that report…
-
Advanced Customization of Microsoft Sentinel Analytics Rules
Join me as we walk through creating a custom Microsoft Sentinel Analytics Rule using KQL to identify suspicious login patterns based on failed attempts. We will explore the different components of creating these custom rules, what tuning looks like, and creating incidents from the rules.
-
Responding to Incidents with Microsoft Sentinel – Part 4 – Automate Research
Today we take a detailed look at building our own Sentinel Playbooks and gathering information on an Incident automatically. Join me as we build automation to update Alerts with detailed IP lookup information as comments. With basic research done automatically, we can save a lot of time!
-
Responding to Incidents with Microsoft Sentinel – Part 2 – Optimize What You See
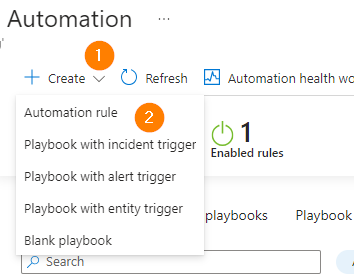
Today, we will explore some enhancements to your Microsoft Sentinel environment. I look at optimizing the ticket queue and working to prevent ticket overload. Join me to explore Automation Rules.
-
Responding to Incidents in Microsoft Sentinel
Join me to explore next steps once you have investigated an incident. Taking action to respond to the threat in Microsoft Sentinel provides excellent automated response capabilities that can be used to respond to threats in real-time. Let’s explore!