kql
-
Microsoft Sentinel Governance Deep-Dive Part 2
This week continues our look at an ongoing set of Governance tasks that we can do to keep our Sentinel instances working smoothly and helping our SOC team stay focused on handling Incidents and threat hunting. Today we continue our detailed look at not only what to review, but walking through the steps together. In…
-
Advanced Customization of Microsoft Sentinel Analytics Rules
Join me as we walk through creating a custom Microsoft Sentinel Analytics Rule using KQL to identify suspicious login patterns based on failed attempts. We will explore the different components of creating these custom rules, what tuning looks like, and creating incidents from the rules.
-
Cost Management & Microsoft Sentinel
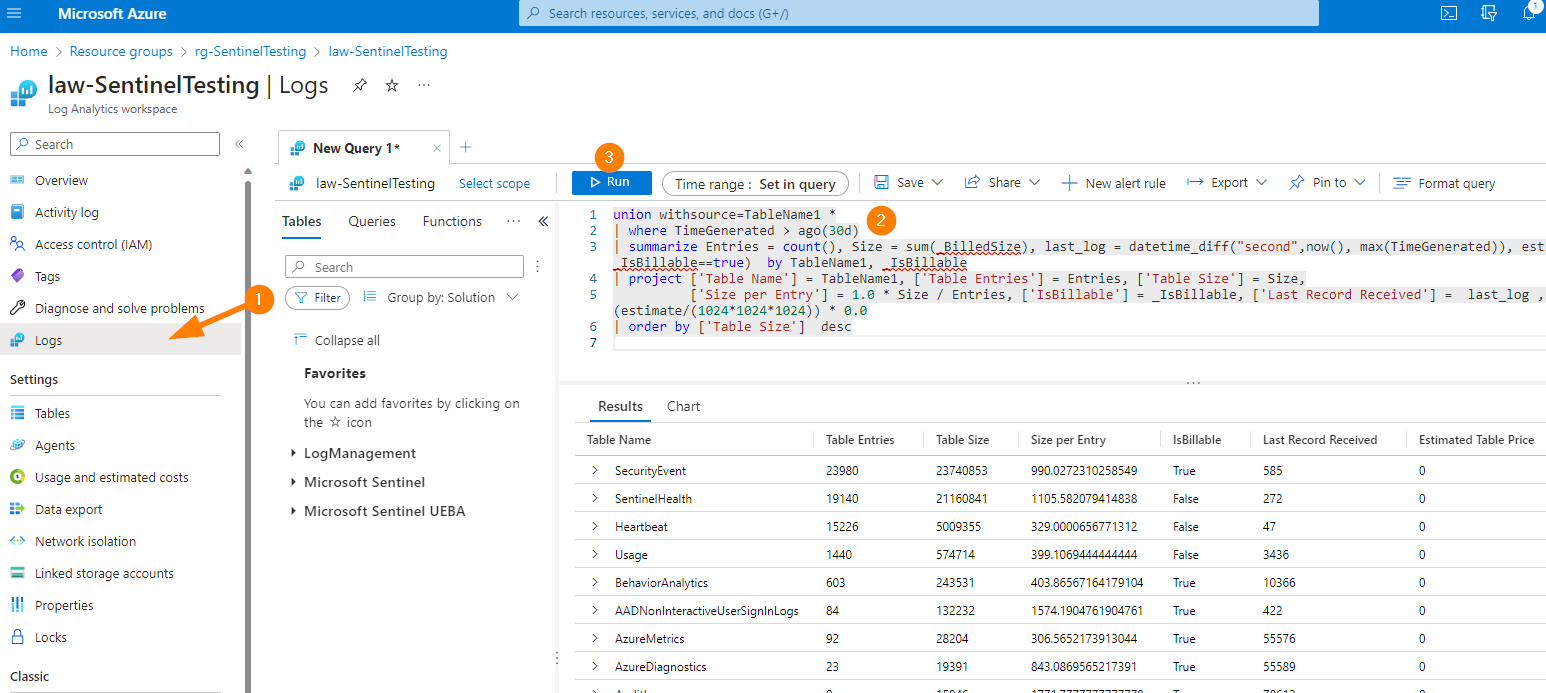
Let’s talk about Microsoft Sentinel and managing costs. With cost being foundational pillar of Microsoft’s Well Architected Framework, part of good governance, and a major driver for product selection of SIEMs; let’s see if we can take some of mystery out of how to get started with managing costs in our favourite SIEM solution!
-
Building Automation Rules with your Sentinel Instance in PowerShell
Today, we explore creating custom Automation Rules in Microsoft Sentinel to help us auto-close low value incidents. Let’s look at how we can automatically close & impact incidents and make it all work using PowerShell!
-
The case of the Duplicate Incidents in Microsoft Sentinel
This is the story about the case of the duplicate incidents in Microsoft Sentinel. Join me as we explore different ways to create incidents, and understand how incidents are created so that we can identify potential duplication.
-
Azure Updates – Number 49 – October 22, 2022
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes. Released October 22, 2022.
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 2 – The Automation Rule
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 2 of How do I create incidents to test with? Today we look at the automation rule and how we can use it trigger our Playbook…
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 1
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 1 of How do I create incidents to test with?
-
Sentinel & Log Analytics – Where is my Data?
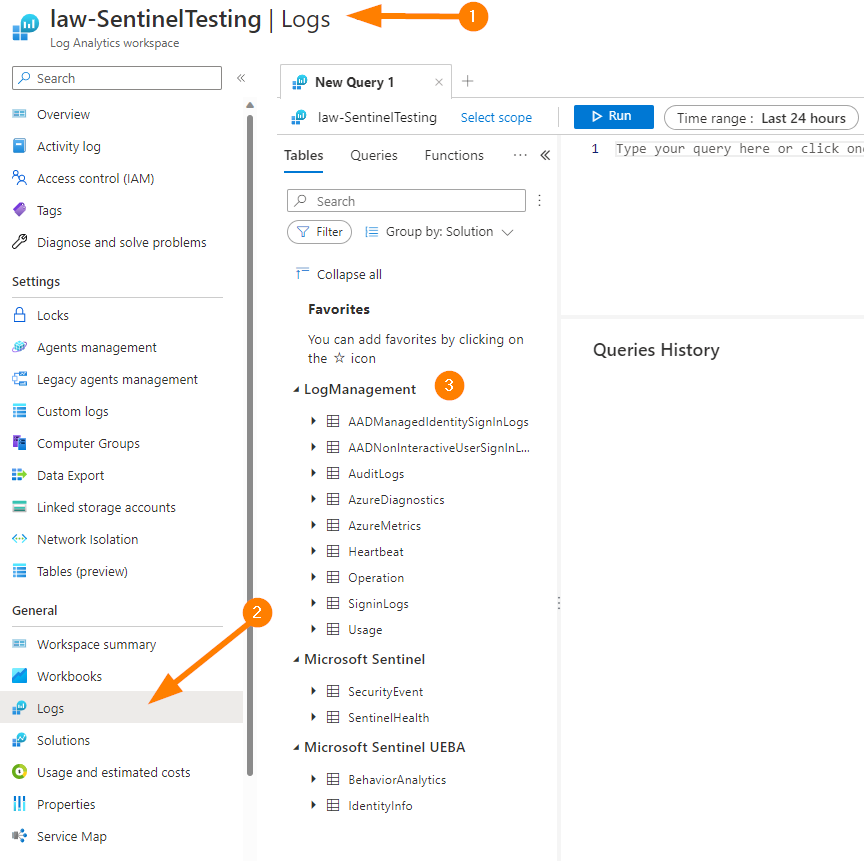
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Where is my Data?
-
Azure Updates – 28 – January 15, 2022
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes. Released January 15, 2022.