security
-
Deploying Microsoft Sentinel with PowerShell
Join me in the latest walkthrough to quickly deploy Microsoft Sentinel so that we can test different scenarios with data connectors, analytics rules, hunting queries, and automations. This is an important idea – testing in non-production – that is often overlooked due to complexity of deployment. Come explore a great way to quickly deploy Sentinel…
-
The case of the Duplicate Incidents in Microsoft Sentinel
This is the story about the case of the duplicate incidents in Microsoft Sentinel. Join me as we explore different ways to create incidents, and understand how incidents are created so that we can identify potential duplication.
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 2 – The Automation Rule
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 2 of How do I create incidents to test with? Today we look at the automation rule and how we can use it trigger our Playbook…
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 1
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 1 of How do I create incidents to test with?
-
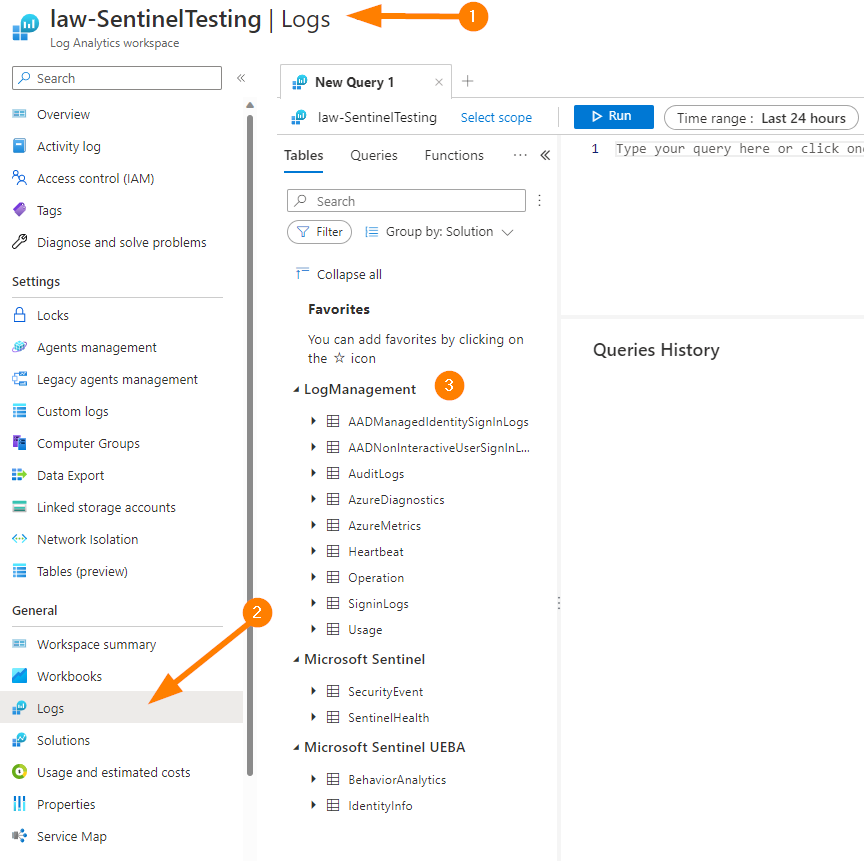
Sentinel & Log Analytics – Where is my Data?
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Where is my Data?
-
Azure Updates – Number 15 – July 17, 2021
A summary update on Azure news that includes updates released from #Microsoft Azure related to #Azure, Architecture, #Compute, and #Sentinel topics. Save time digging around to find recent releases and changes. Released July 17, 2021.
-
Azure Tags – Tagging Best Practices
In the final installment of Azure Tagging, today we wrap up our strategy with some best practices. Join me as I cover cost management benefits, consistency, automation, and governance topics around tagging in Azure.
-
Azure Tags – Tagging Strategy
Today, we extend our discussion of why to tag – and look at tagging strategy in Azure. We look at tagging goals of cost monitoring, app owner improvements, security, and data classification; and build our tags out…
-
Azure Updates – Number 3 – Feb 13, 2021
A summary update on Azure news that includes updates released from Microsoft Azure related to Azure, Architecture, Compute, and Sentinel topics. Save time digging around to find recent releases and changes. Released Feb 13th
-
Microsoft Cloud Identity – MFA in Microsoft Cloud
Today Microsoft Cloud Quick Fix chats with Andrew Lowes from AzureTracks about Multi-factor Authentication in the Microsoft Cloud and recent finding that 78% of Microsoft 365 administrators do not have multi-factor authentication (MFA) activated!