loganalytics
-
Monitoring and Analytics with Azure Monitor
In modern cloud environments, maintaining the health and performance of applications is critical. Azure Monitor provides a full-stack monitoring solution that enables organizations to track metrics, diagnose issues, and gain deep insights into their applications and infrastructure. Whether monitoring virtual machines (VMs), Kubernetes clusters, databases, or application services, Azure Monitor ensures optimal performance with proactive…
-
Microsoft Sentinel Governance Deep-Dive Part 2
This week continues our look at an ongoing set of Governance tasks that we can do to keep our Sentinel instances working smoothly and helping our SOC team stay focused on handling Incidents and threat hunting. Today we continue our detailed look at not only what to review, but walking through the steps together. In…
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 2 – The Automation Rule
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 2 of How do I create incidents to test with? Today we look at the automation rule and how we can use it trigger our Playbook…
-
Sentinel & Log Analytics – How to Create Incidents to Test with – Part 1
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Part 1 of How do I create incidents to test with?
-
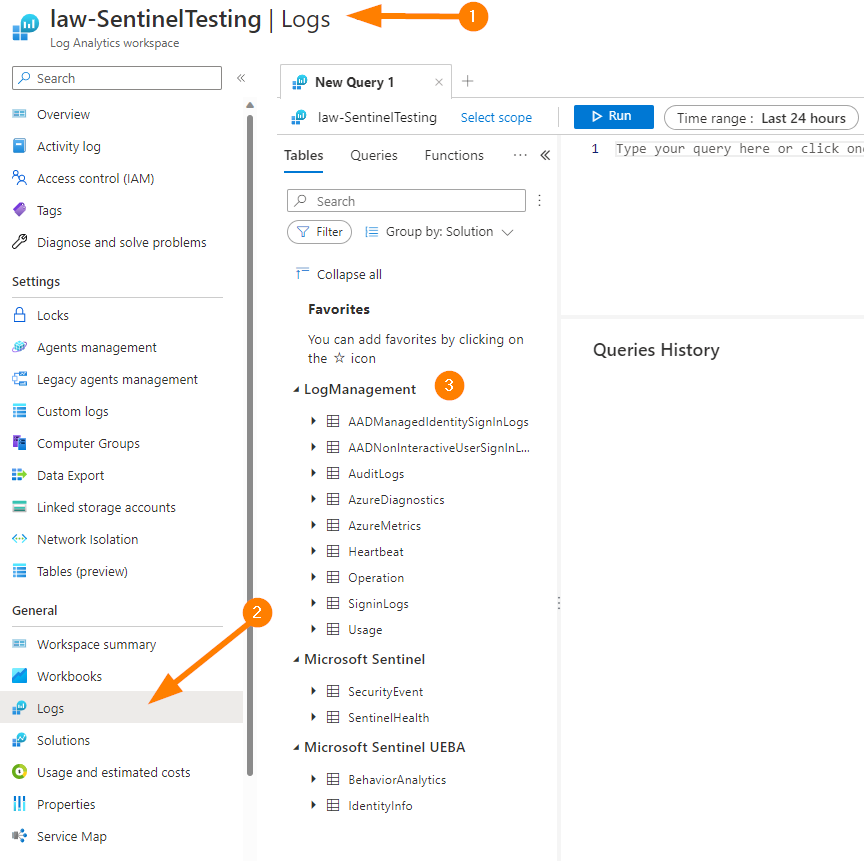
Sentinel & Log Analytics – Where is my Data?
Today, I’d like to talk about using Microsoft Sentinel and address a common question that many teams have when they are starting to work with the Sentinel SIEM/SOAR solution….Where is my Data?